OutageAlerts
AO3 is down again for “preventative maintenance” after its security incident
Archive of Our Own went offline again on Thursday, 19 November, four days after it came back from a security incident. Here’s what the Organization for Transformative Works has said, and what AO3 users should do.
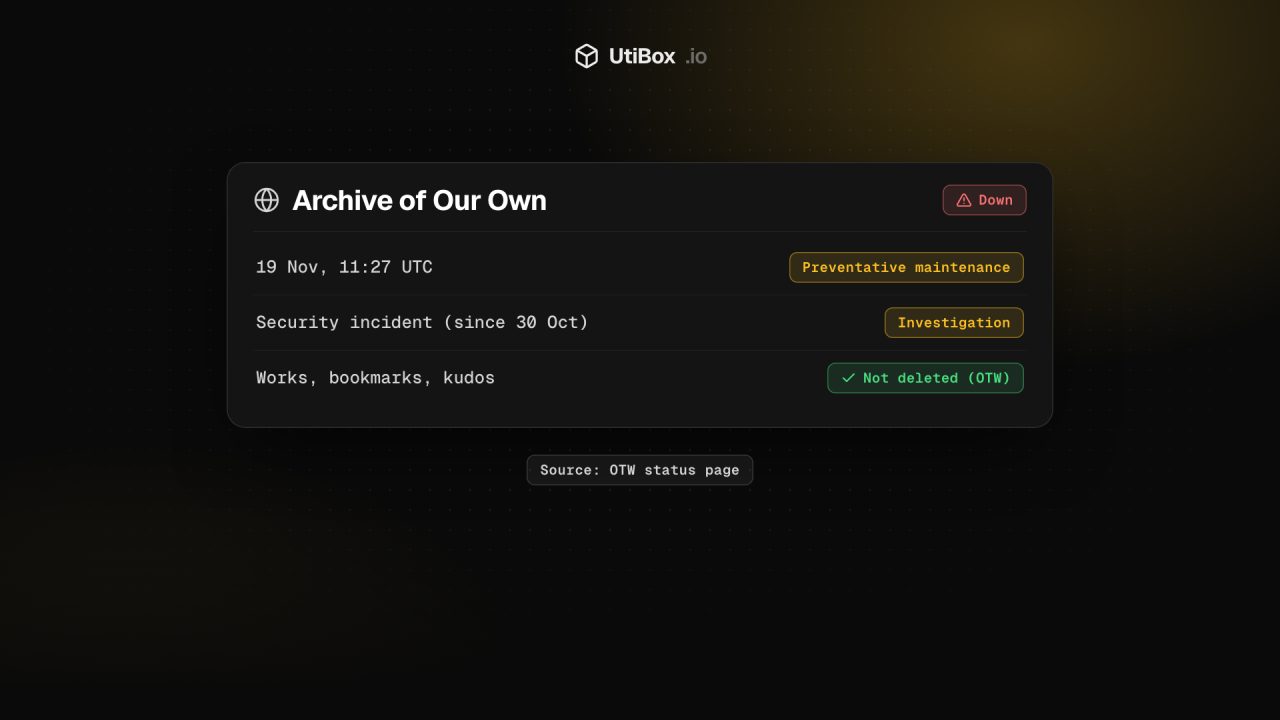
Illustration: UtiBox
Outage
OngoingArchive of Our Own is down for preventative maintenance. Provider-reported by the Organization for Transformative Works.
- Affects
- AArchive of Our Own (AO3)
- Last check
- Up · 86 ms6 min ago
- Provider says
- Outage reportedOTW status (Archive of Our Own)
- Posted
- Ends
- Not known yet
What’s happening
Archive of Our Own (AO3), the non-profit fan-fiction archive, went offline again on the morning of Thursday, 19 November 2026. OTW calls it “preventative maintenance” and hasn’t said what the work involves or how long it will take. Fanlore, OTW’s fan wiki, is also down for maintenance today.
OTW posted the update under the same incident it opened on 29 October, when AO3 first went down. It hasn’t said whether today’s maintenance is connected to the security incident below, and we won’t guess.
How we got here
All of this comes from OTW’s own status page:
- 29 October: AO3 went down for maintenance. Later that day OTW estimated restoration would take “around 2 weeks but it could be up to 4 weeks.”
- 30 October: OTW said it had “detected evidence of a security incident on AO3.” It said no AO3 data had been deleted. It also said that while it didn’t believe the user database was stolen, it was “unable to rule it out”. The database may include usernames, email addresses, IP addresses and hashed passwords.
- 15 November: “AO3 is now up!” The site came back early with some features switched off: icons, importing works from other sites, and downloads in formats other than HTML. Draft deletion was paused.
- 17 November: the invitation queue re-opened, so new accounts could be created again.
- 19 November, 11:27 UTC: down again for preventative maintenance.
What AO3 users should do
- Change your AO3 password once the site is back, as OTW recommended on 30 October, if you haven’t already.
- Change any other password that’s the same as your AO3 one. Reused passwords are what attackers try first. Our password generator makes a strong new one.
- Your works are safe, according to OTW: no works, bookmarks or kudos were deleted, and draft deletion was paused while the site was down.
- Be wary of “AO3” emails asking you to log in. OTW said some genuine notification emails queued before the outage were released in November. Even so, go to AO3 by typing its address yourself, not through a link in an email.
How to know when it’s back
- OTW’s official status page: otwstatus.org (opens in a new tab)
- Our AO3 status page shows OTW’s report beside our own check of the website. Its banner and this alert close automatically once OTW marks the site as working again.
Sources
- Organization for Transformative Works: OTW status page (opens in a new tab), incident “AO3 Down for Maintenance” (updates from 29 October to 19 November 2026)
Related


More from Alerts

WarningAlerts
GPUStack auth bypass exploited: why “trust localhost” fails behind a proxy
GPUStack versions before 2.2.0 treated any request from 127.0.0.1 as the administrator. Behind a reverse proxy on the same server, that’s every request. CISA lists the flaw as exploited. Upgrade,…

WarningAlerts
Brotli decoder flaw is being exploited: update libbrotli, Node.js and .NET
A bug in Google’s Brotli decompression library lets a crafted compressed stream corrupt memory, and CISA says it’s being exploited. Fixed in Brotli 1.0.10, 1.1.1 and 1.2.1, Node.js 22.23.4, 24.22.1…

WarningAlerts
Chrome zero-day CVE-2026-125350 is being exploited: update to 157.0.8103.50
Google fixed a use-after-free bug in Chrome’s XML handling on 9 November 2026, saying an exploit exists in the wild. Update Chrome to 157.0.8103.50 or later, and don’t forget Edge, other Chromium…


