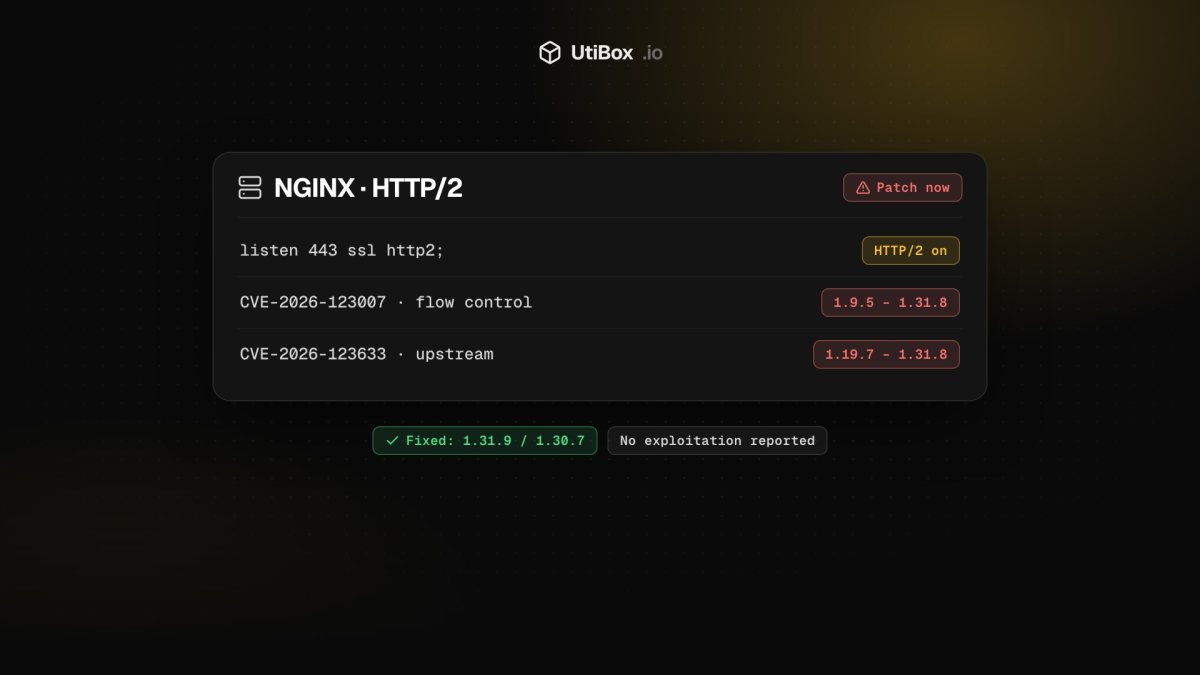
Critical NGINX HTTP/2 vulnerabilities disclosed: what website owners must check
NGINX 1.31.9 and 1.30.7 fix CVE-2026-123007 and CVE-2026-123633, two HTTP/2 memory-safety flaws that can lead to code execution. Here’s who is affected, how to check your server, and the stop-gap if you can’t patch…